
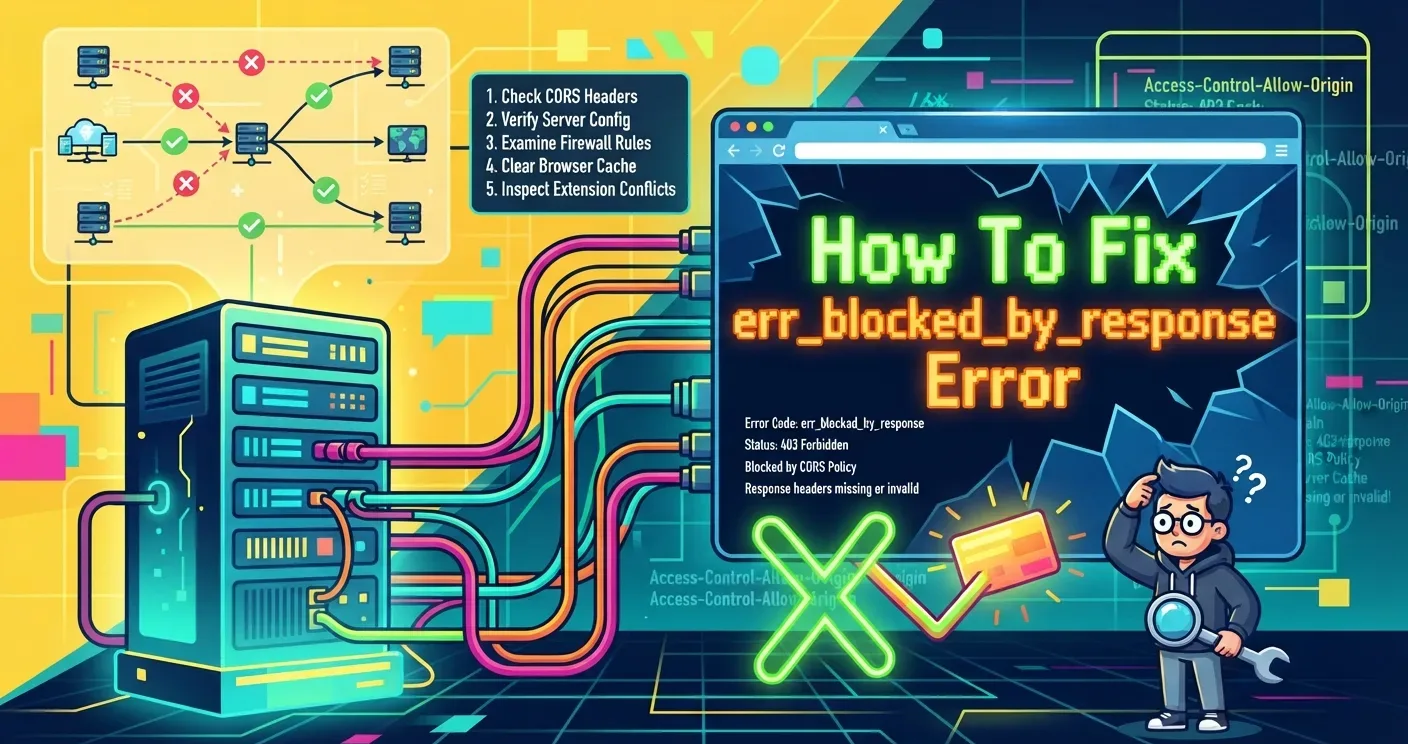
err_blocked_by_response appears when Chrome throws away a reply it already received. The server answered. A rule then stopped that answer from rendering. Scripts, fonts, images and entire pages fail this way.
The cause sits in one of three places: your browser, your network, or the server. The checks below tell you which.
What err_blocked_by_response Means in Chrome
The message comes from the browser. Chrome reads the response headers, decides something breaks a rule, and drops the resource before it reaches the page.
You will meet it two ways. A full-screen failure when the main document gets blocked, or a red line in the DevTools console reading net::err_blocked_by_response followed by the file that never loaded.
That difference narrows the hunt. Page-wide blocks usually trace to header rules such as X-Frame-Options. A single failed file usually traces to CORS or an extension. It behaves nothing like err_cache_miss, which involves data Chrome saved earlier rather than the current reply.
What Causes the err_blocked_by_response Error
Gaps in the CORS Policy
Cross-Origin Resource Sharing decides whether one domain may read files kept on another. Write those headers badly and the browser refuses the response.
Say your page loads a weather widget pulling readings from api.weather.com. If that API never returns Access-Control-Allow-Origin: https://yourdomain.com, Chrome discards the reply. The repair belongs to whoever runs the API.
Subdomains hit the same wall. A request from www.example.com to api.example.com fails when the headers skip the calling origin.
Misconfigured Security Headers
Content-Security-Policy and X-Frame-Options exist to refuse responses. CSP lists which sources may supply scripts, styles and fonts, so anything outside that list gets dropped.
Google Fonts breaks this way often. One narrow CSP directive refuses the font files and the error lands in your console. Absent or malformed Content-Type and Strict-Transport-Security headers produce the same result.
Browser Extensions Blocking Responses
Ad filters and privacy tools sit between the request and the reply. uBlock Origin, AdBlock and Ghostery cut off calls to hosts they read as advertising or tracking.
Analytics scripts and marketing pixels are the usual casualties. Several privacy and security add-ons filter traffic the same way. Incognito mode settles the question in seconds.
Network, Firewall and VPN Restrictions
A corporate firewall, a proxy machine, a VPN or a national filter can hold a response back before Chrome ever sees it.
Staff on locked-down office networks meet this daily. So do readers in regions where outside domains get filtered, which is why methods for reaching restricted sites keep circulating.
Broken Endpoints or Script Errors
One typo in a fetch call sends a malformed request. The server answers with a fault and the browser drops the file. Developers see this most often right after an API change.
How to Fix err_blocked_by_response: 6 Methods
1. Clear Cache and Cookies
Stale site data clashes with fresh responses. Press Ctrl + Shift + Delete, tick cached images and cookies, then reload the page.
This walkthrough on clearing Chrome cache and cookies covers desktop, Android and iPhone. If pages still misbehave, flush Chrome’s DNS records at chrome://net-internals/#dns.
2. Switch Off Your Extensions
Open chrome://extensions and toggle items off one at a time, ad blockers first. Reload the window after each change.
Once the guilty one shows itself, update it or delete it. The same panel handles installing Chrome extensions again later if you need the tool back.
3. Inspect the CORS Rules on Your Server
Right-click the page, pick Inspect, open the Network panel, then reload. Click the failed request and read its response headers.
Check the Access-Control-Allow-Origin line. If your domain is missing, the server will not hand the file across. Add the correct header through your hosting panel on sites you own. Write to the owner when an outside API is at fault.
4. Review Firewall and Proxy Settings
Turn the firewall off briefly and reload. A page that suddenly works points straight at the rule set. These steps for letting Chrome through firewall and antivirus settings fix it without leaving your machine exposed.
Proxies deserve the same look. Misrouted traffic surfaces as a blocked response, so check your Chrome proxy configuration before blaming the site.
5. Update or Reinstall the Browser
Old builds throw faults that current ones do not. Go to Help, then About Google Chrome, and relaunch if an update waits. Chromebook users check About ChromeOS instead, since the browser updates with the system.
Should the error survive, pull a fresh copy from the official site and install it over the damaged build.
6. Trace the Cause in Developer Tools
Press F12, open the Network panel, reload, and find the requests marked red. Status codes and response headers name what refused the file.
A blocked font points at CSP. A blocked API call points at CORS. A reply that arrives empty sits closer to net::err_empty_response and belongs to the host. Hand your findings to whoever administers that server.
When err_blocked_by_response Keeps Coming Back
Repeat cases nearly always trace to headers. Add a new API, embed, or CDN rule without updating CORS and CSP, and the block returns within a day.
Files served from a domain you do not control sit outside your reach. Send the failing URL and the console text to its owner. That is faster than another round of browser tweaks, and it stops the error for every reader at once.
FAQs
What does err_blocked_by_response mean?
It means Chrome received a server response and then refused to use it. A security rule such as CORS, Content-Security-Policy or X-Frame-Options stopped the file from loading on the page.
What is the difference between err_blocked_by_response and err_blocked_by_client?
err_blocked_by_response comes from server headers refusing the reply. err_blocked_by_client comes from your own machine, usually an ad blocker or security extension cutting the request before it leaves.
What do Reddit users recommend for err_blocked_by_response?
Reddit threads point to the same first move: test in Incognito. If the page loads there, an extension is blocking it. Reddit developers then check CORS and CSP headers in DevTools.
Why does Reddit itself show err_blocked_by_response?
Embedded Reddit content fails when X-Frame-Options blocks the iframe, or when an ad blocker refuses Reddit’s tracking scripts. Open the link directly instead of through an embed or preview wrapper.
Can a VPN fix err_blocked_by_response?
Sometimes. A VPN helps when a network filter or regional block stops the response. It changes nothing when the cause is a CORS header, a CSP rule or a browser extension.
